- Details
Regulatory Framework
Security Technical Instruction (ITS) of Information Systems Security Audit
Security Technical Instruction (ITS) in accordance with the National Security Framework
Security Technical Instruction (ITS) of State of Security Report
Security Technical Instruction (ITS) Security Incidents Notification
Several documents have been developed to correct the errors detected:
Table in section 2.4 of Annex II
Errors have been detected in the publication of Royal Decree 951/2015 of 23 October. These are found in the following sections:
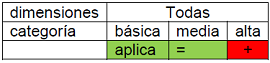
1) Security architecture: inconsistency in the table and the section. A + is missing in section 4.1.2 as there is an increase in requirements.
It says in section 4.1.2:
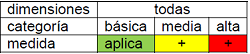
It should read:
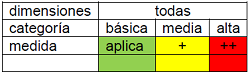
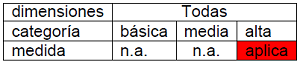
2) Certified components: error in the compilation table and the section on cell color. This color should be red when the measure only applies to this HIGH category.
It says in section 4.1.5:
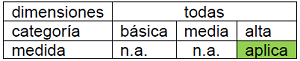
It should read:
3) Metric systems: inconsistency between the table and the section.
The table in section 2.4 of Annex II reads as follows:

It should read:

4) Deletion and destruction: inconsistency between the compilation table and the section.
It says in section 5.5.5:
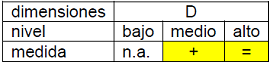
It should read:
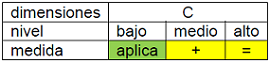
5) Application development: where it says low, medium, high category; it should say basic, medium, high category).
It says in section 5.6.1:
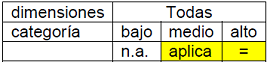
It should read:
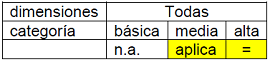
6) Protection of web services and applications: where it says level, it should say category.
It says in section 5.8.2:
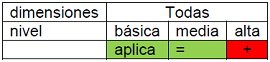
It should read:
You can find a more detailed explanation of the errors detected in the following document.